The Cyber Security Authority (CSA) and the National Information Technology Agency (NITA) have warned organisations in Ghana about two critical security flaws that could expose their websites and servers to cyberattacks.
In a joint statement issued on Thursday, October 22, 2026, the agencies urged government institutions, businesses and website owners to install security updates immediately.
The flaws, known as “PHP2Shell”, affect PHP, a programming language widely used to run websites and online services. They are identified by the codes CVE-2026-109618 and CVE-2026-109619.
According to the agencies, hackers could exploit the flaws to take control of affected servers without a username or password.
“Successful exploitation could expose sensitive information, disrupt services, and enable further attacks against an organisation’s network,” the statement warned.
The PHP Project has released security fixes for versions 8.2.35, 8.3.36, 8.4.27 and 8.5.12. The agencies have urged affected organisations to install the correct updates or move to a later supported version.
They stressed that updating website themes and plugins alone would not fix the problem.
“Updating website themes or plugins alone does not resolve vulnerabilities in the underlying PHP software,” the statement said.
The agencies have advised organisations to check their websites, applications and servers for affected software. They have also urged administrators to prioritise systems connected to the internet and those supporting essential public services.
Where an immediate update is not possible, organisations have been advised to take affected services offline until they can be secured.
The statement also called on organisations to check their systems for signs of unauthorised access. These include unusual activity, unknown administrator accounts and unexpected changes to website files.
The agencies further directed government institutions to take action within seven days and report the measures taken to the CSA and NITA.
“Heads of government institutions should ensure that their ICT teams and service providers act urgently,” the statement said.
NITA will coordinate technical support for government digital services, while the CSA will oversee cybersecurity incident reporting and response.
Government institutions have also been asked to keep updated records of their digital systems and appoint officers to coordinate the response under NITA’s Government Digital Assurance Programme (GovDAP).
The agencies have warned the public to be careful with messages claiming to offer PHP security updates. Such messages could be used to trick people into downloading harmful files or sharing sensitive information.
“Be cautious of messages asking you to download a ‘PHP security update,’ disclose passwords or provide payment details,” the statement cautioned.
Website owners have been advised to obtain updates only from official software sources or verified service providers.
The agencies urged all affected organisations to treat the warning as urgent and take steps to protect their systems.
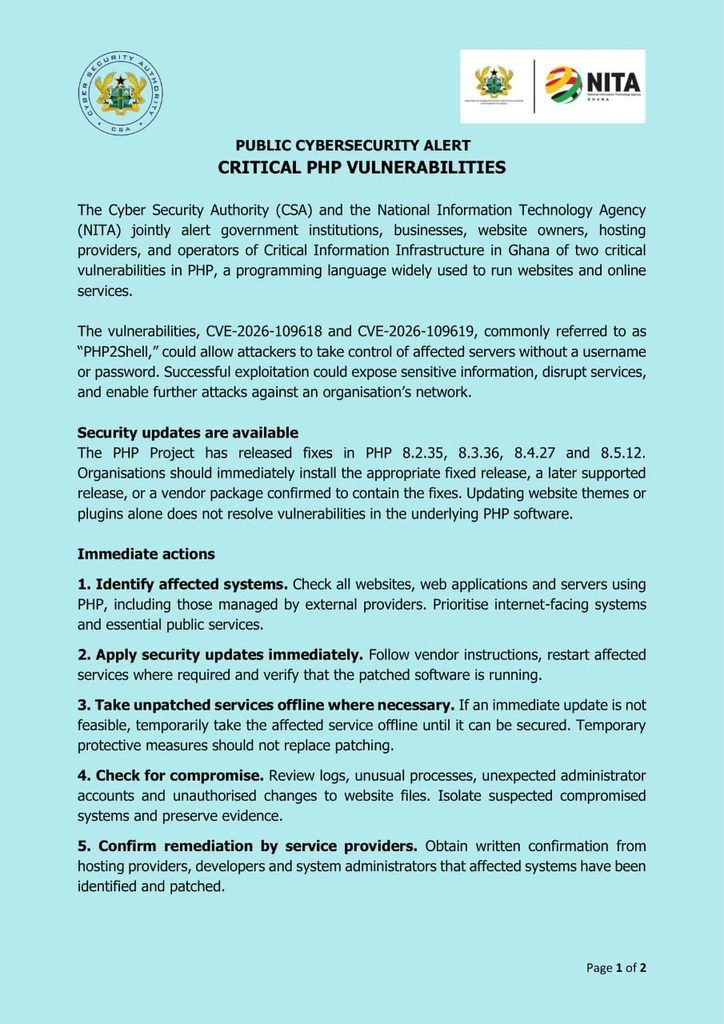
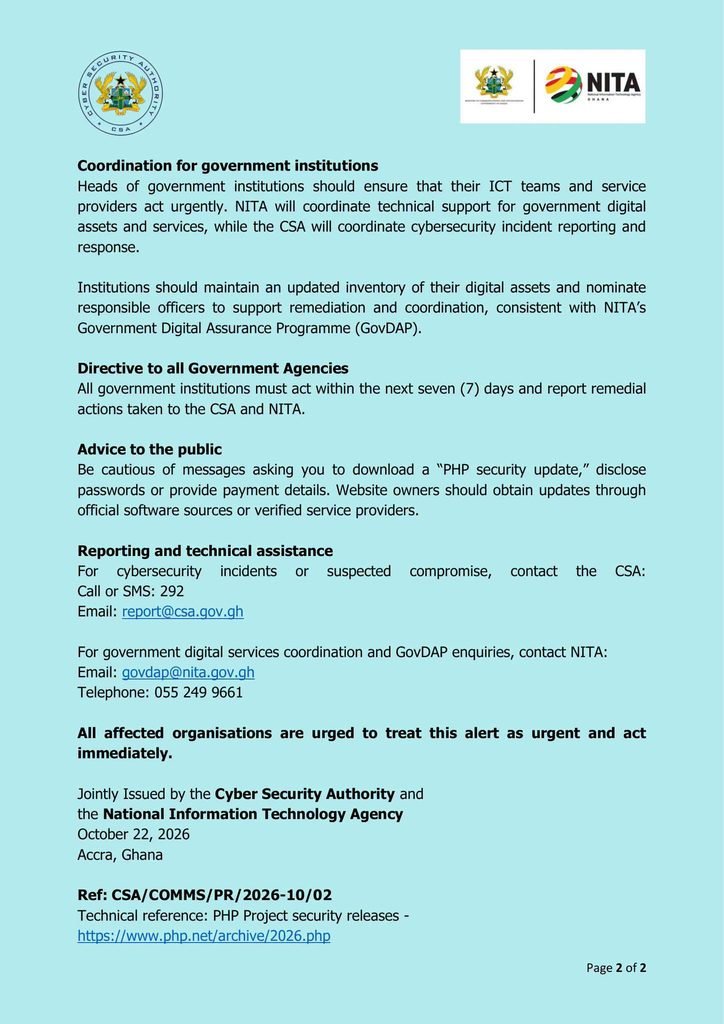
Read the statement below: